A platform direction built around open infrastructure
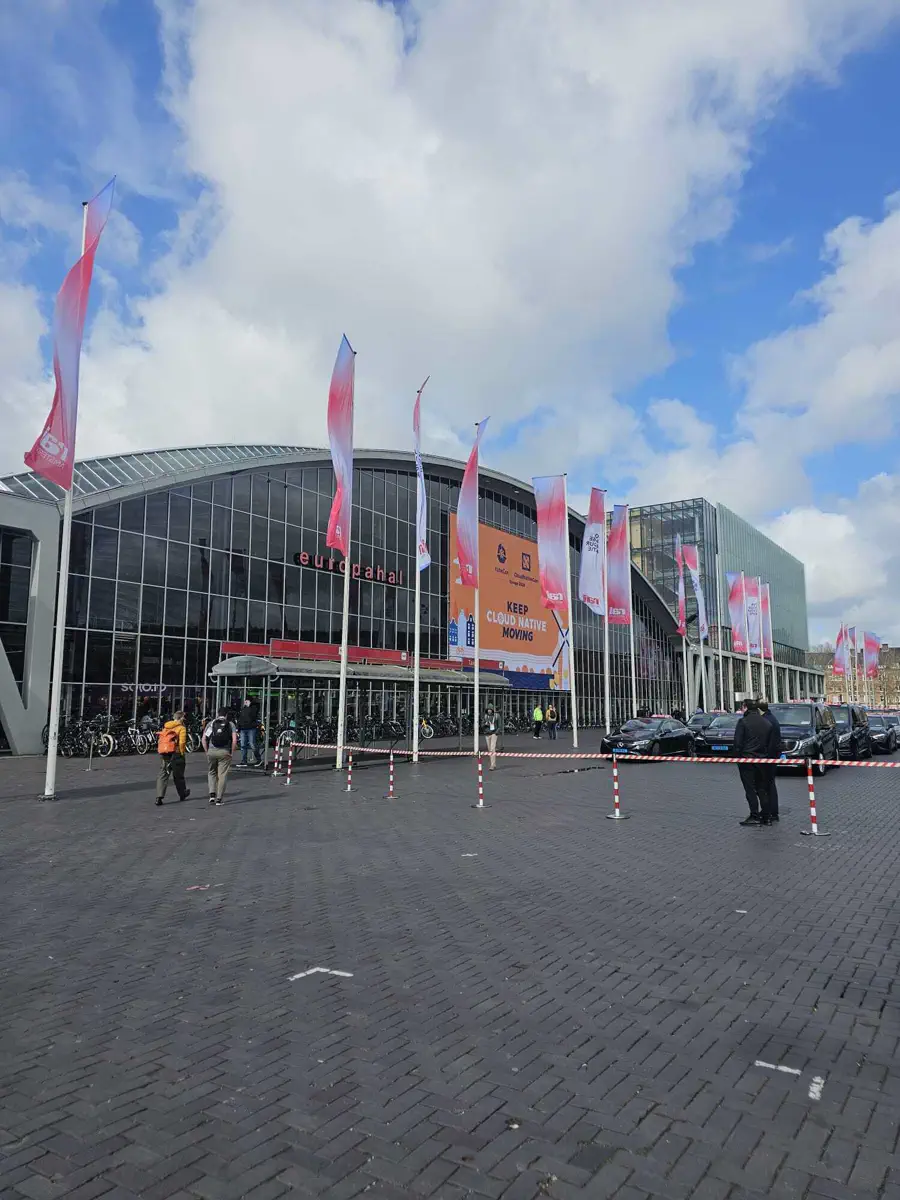
Across the selected articles, Safespring presents digital sovereignty, Kubernetes operations and AI infrastructure as connected concerns. The provider describes its Kubernetes Engine as a self-service service on Safespring Compute with a managed control plane, Talos Linux, Cilium networking, Gateway API support, Cinder CSI storage, OIDC authentication and GPU-capable workers. It also explicitly leaves workload observability, RBAC conventions, application resilience and several other upper-layer responsibilities to customers. In its account of KubeCon + CloudNativeCon Europe 2026, Safespring argues that Kubernetes is becoming a control plane for AI infrastructure, highlighting GPU resource allocation, distributed inference, multicluster networking, GitOps and AI-oriented observability. Its article on digital control adds a legal and governance dimension: organizations should understand jurisdiction, subcontractors, transfer mechanisms, portability and exit options rather than treating sovereignty as a product label. These are Safespring’s descriptions and assessments; the supplied material does not independently validate service performance or operational outcomes.
The emerging trend: sovereignty moves into platform engineering
The strategic pattern is a shift from sovereignty as data location toward sovereignty as retained decision-making power. Safespring is positioning open interfaces and recognizable infrastructure components—particularly OpenStack, Kubernetes and S3-compatible storage—as ways to make dependencies more visible and future migration more feasible. Its technology direction combines that portability argument with a managed Kubernetes boundary: the provider operates selected cluster foundations while customers retain control over workload architecture and operational tooling. AI reinforces this direction because model access, GPU scheduling, data processing and foreign legal decisions can all become infrastructure dependencies. For Sweden, Norway and the wider Nordic market, the proposition is therefore not merely local hosting. It is a European-controlled platform approach intended to connect regulatory governance, cloud-native operations and accelerated computing without placing every layer behind a proprietary abstraction.
Clear boundaries do not eliminate implementation risk
The approach has important limitations. Open standards can reduce switching friction, but they do not by themselves guarantee portability: applications can remain tied to specific storage behavior, identity models, network policies, operational processes or AI models. Safespring’s documented Kubernetes boundary also leaves customers responsible for observability, log retention, alerting, workload SLOs, RBAC design, stateful application behavior and GPU cost controls. That demands capable platform teams even when the control plane is managed. The supplied articles provide architecture descriptions and strategic arguments, but no independently tested availability, performance, migration effort, support outcomes or total-cost comparisons. Buyers should also avoid equating Nordic or European operation automatically with complete legal insulation; contracts, corporate control, subprocessors, remote access and dependencies elsewhere in the stack still require examination. Finally, Safespring’s KubeCon conclusions about AI maturity and industry direction are conference-derived observations rather than evidence that every enterprise workload is ready for AI-enabled production operations.
Nordic decision guide and sources: Safespring on digital control, Safespring’s KubeCon 2026 recap and Safespring’s Kubernetes Engine guide
For Nordic IT decision-makers, Safespring merits evaluation where jurisdictional control, open infrastructure and Kubernetes are joint requirements rather than separate procurement topics. The strongest aspect of the proposition is its stated service boundary: buyers can identify what the provider says it manages and what remains their responsibility. A proof of concept should test identity integration, network and storage behavior, failure handling, observability deployment, GPU workload operations and export or migration procedures. Procurement teams should map legal entities, subprocessors, support access and exit terms alongside the technical architecture, then compare that complete operating model with both self-managed OpenStack-based environments and larger managed-cloud alternatives. The relevant source material is Safespring’s discussion of digital control and structural dependencies, its KubeCon + CloudNativeCon Europe 2026 observations and its detailed account of the Safespring Kubernetes Engine responsibility boundary. Taken together, they indicate a coherent Nordic strategy: sovereign cloud is being framed as an architectural and operational discipline, with Kubernetes serving as the bridge to AI infrastructure.
